
AI governance is often confused with an AI policy or an ethics statement. These documents can be part of a governance program, but they are only one part of it.
A practical framework should help an organization answer four basic questions:
In practice, this usually means maintaining:
Organizations should maintain a current record of the AI systems they build, purchase, or use through existing software. This should include AI features built into business applications and other tools used by individual teams.
Each AI system should be assessed according to its purpose, the people it affects, the decisions it influences, and the potential consequences of an error.
A simple internal productivity tool may require a different level of review from an AI system used in recruitment, lending, healthcare, or other sensitive areas.
Every AI system should have a clearly identified owner. This person or team is responsible for making sure the system follows the organization’s requirements and that issues are addressed when they arise.
Governance continues after deployment. Organizations need appropriate monitoring, documentation, and audit records to understand how a system performs over time and whether its use has changed.
These elements turn AI governance from a written policy into a process that can be followed across the organization.
The way companies use AI has changed considerably. Many organizations now have AI tools operating across several departments, with some applications introduced through existing software rather than through a central AI team.
For example, a customer service team may use an AI summarization feature, a finance team may use AI-assisted analysis, and a recruitment team may use AI features within its hiring software.
When these tools are managed separately, it becomes harder to maintain a complete view of where AI is being used and what level of oversight each system needs.
AI is also becoming part of business decisions. Its output may influence customer interactions, employee processes, financial decisions, or other important activities. This makes clear ownership, testing, documentation, and ongoing monitoring increasingly important.
Regulatory requirements are another reason enterprises are putting more attention on AI governance. Organizations need to understand which rules apply to their AI systems and how those requirements affect their processes.
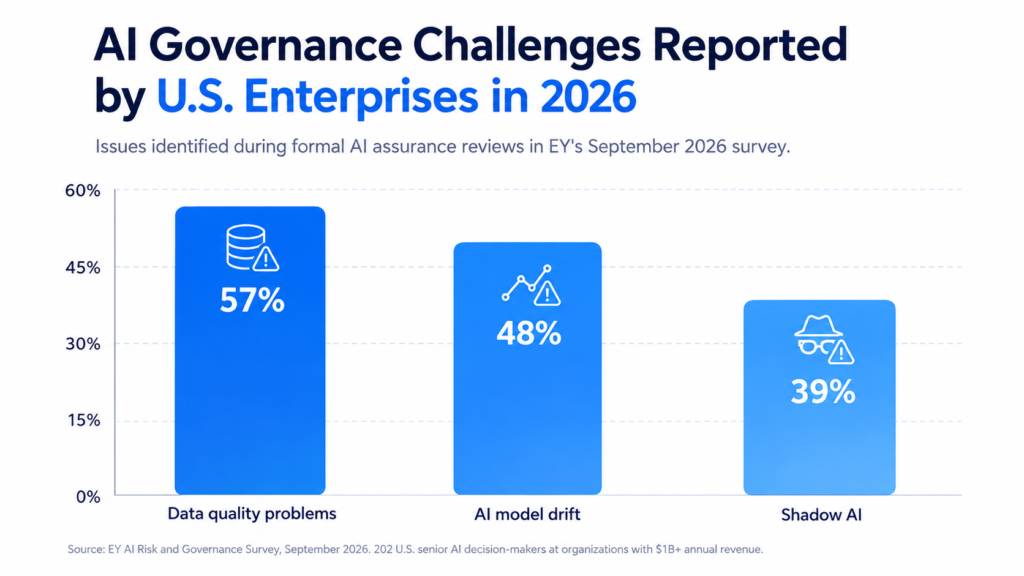
These figures come from EY’s September 2026 survey of 202 senior AI decision-makers at U.S. companies with at least $1 billion in annual revenue.
Several regulations and standards provide useful guidance for organizations developing an AI governance program. Their purpose and legal status are different, so companies should understand what each one actually requires.
The EU AI Act is being implemented in stages. Different requirements apply at different points in the implementation timeline, depending on the type of AI system and the organization’s role.
For enterprises operating in or serving the European market, governance processes should take these requirements into account when assessing AI systems, documenting their use, assigning responsibilities, and establishing controls.
The implementation timeline has also changed for certain high-risk AI requirements. Organizations should therefore check the current regulatory position when planning their compliance work rather than relying on an older implementation schedule.
Transparency requirements also form an important part of the framework, particularly for certain AI-generated or AI-mediated content and interactions.
The NIST AI Risk Management Framework (AI RMF) provides a practical approach to identifying and managing AI-related risks.
Its four main functions are:
The framework can help organizations establish responsibilities, understand potential risks, evaluate AI systems, and manage those risks throughout their lifecycle.
Although the NIST AI RMF is voluntary, its structure can be useful for organizations developing their own internal governance processes.
ISO/IEC 42001 provides requirements for an AI management system. It gives organizations a structured way to establish, maintain, and continually improve their approach to managing AI.
Certification can provide useful evidence that an organization has established a formal management system. However, certification should not be treated as an automatic replacement for specific legal or regulatory requirements.
Organizations should assess the applicable regulations and standards separately and determine how they fit into their overall governance program.
The OECD AI Principles provide broad guidance around responsible AI, including areas such as transparency, accountability, robustness, security, and human-centred values.
They are not a substitute for legal compliance, but they can help organizations define the principles that guide their internal AI policies and governance practices.
While specific requirements vary by organization and use case, several principles appear consistently across established approaches to AI governance.
Every AI system should have clearly defined responsibility.
The organization should know who approves the system, who oversees its use, who reviews its performance, and who is responsible for addressing problems.
A governance committee can provide direction and oversight, but individual systems still need clear ownership.
Organizations should document what they know about the AI systems they use.
For third-party systems, this may include the model or service being used, the type of data being provided, the intended purpose, testing results, known limitations, and the controls surrounding its use.
The level of explanation required should reflect the system’s purpose and risk.
Fairness should be considered throughout the AI lifecycle rather than only during initial testing.
Organizations can define appropriate fairness measures, test systems using representative data, and review results periodically. Changes in data, users, or the way a system is used can affect its performance over time.
AI systems can process large amounts of business and personal information, making privacy and security important parts of governance.
Organizations should consider access controls, data protection, encryption, data minimization, and appropriate handling of personal information before data is sent to an AI service.
These controls should be built into normal processes wherever possible rather than depending entirely on individual users to remember them.
Human oversight should match the risk and purpose of the AI system.
High-impact applications may require defined points where a qualified person can review, intervene, override, or stop an AI-supported process.
The organization should also maintain appropriate records of important interventions and decisions.
Building a governance framework is an ongoing process. Organizations commonly face challenges when they try to apply governance consistently across different teams and systems.
A policy may require certain safeguards, but those safeguards also need to be reflected in day-to-day processes and technical controls.
When responsibility is spread across several departments without a clearly accountable owner, it can become difficult to make decisions or respond to issues.
The way an AI system is used can change over time. A tool originally used for internal work may later become part of a customer-facing process, which may require a fresh risk assessment.
AI governance should continue from initial planning through deployment and ongoing monitoring. Reviewing a system only before launch leaves important parts of its lifecycle outside the governance process.
Employees may start using AI features within existing software or external tools. Organizations need a practical process for identifying these systems and bringing them into the appropriate governance process.
Enterprises do not need to create an enormous governance program from the beginning. A structured AI governance and compliance approach can start with a clear view of existing AI use and gradually introduce the controls that match the organization’s needs.
Identify the AI systems currently being developed, purchased, or used across the organization. Include AI features within existing business software.
Review each system based on its purpose, users, data, decisions influenced, and potential impact. Organizations that need a more structured assessment can also review their existing AI governance processes, controls, documentation, and responsibilities before creating a longer-term implementation plan.
Give each AI system a clearly identified owner who remains responsible for oversight after deployment.
Set documentation, testing, approval, and monitoring requirements according to the risk of each use case.
Introduce appropriate reviews throughout the lifecycle, from initial planning and data assessment to testing, approval, deployment, and monitoring.
Track relevant performance, changes in use, data quality, security issues, and other indicators that could affect the system’s risk.
Define what happens when an AI system produces an unexpected result, violates an internal requirement, or creates a significant risk.
The process should identify who investigates the issue, who communicates internally or externally when required, and how lessons from the incident are incorporated into future reviews.
AI regulations, standards, technologies, and business use cases continue to change. A regular review cycle helps organizations keep their governance practices current.
AI governance generally involves several departments. Legal and compliance teams may focus on regulatory requirements, security teams on data protection and access, technical teams on system evaluation, and business teams on the outcomes of specific applications.
The important part is having clearly defined responsibilities and an accountable owner for each AI system.
ISO/IEC 42001 certification should not be treated as a complete replacement for EU AI Act requirements.
Organizations should assess the specific obligations that apply to their AI systems and understand how relevant standards and management systems can support their compliance work.
The first step is usually to understand where AI is already being used.
An organization should identify its AI systems, determine which applications require greater oversight, assign responsibility, and establish the basic policies and controls needed for those systems.
The timeline depends on the organization’s size, number of AI systems, existing policies, technical controls, and regulatory requirements.
A focused governance program can begin with inventory, risk assessment, ownership, and monitoring. More mature programs may require additional time for documentation, controls, audits, training, and certification.
No. Governance also matters when organizations use AI systems provided by third parties.
Companies should understand how vendor AI tools are used, what information is shared with them, what controls are available, and what responsibilities remain with the organization using the system.
For many enterprises, the first step is simply understanding what AI systems are already being used across the organization.
From there, companies can identify the level of risk associated with each system, assign ownership, review existing controls, and establish a governance process that fits their operations.
A practical AI governance program should support the business rather than create unnecessary barriers to useful technology. The right structure gives teams a clear way to evaluate AI applications, manage their responsibilities, document important decisions, and review systems as their use changes.
Wronit can help enterprises assess their AI governance needs and build practical processes around risk assessment, compliance, documentation, controls, and ongoing oversight.
Explore AI Governance & Compliance Services →